Security Preferences
The Security Preferences section of the Account Info page is designed to give Account Administrators (or Security personnel) a way to manage and enforce the security preferences and guidelines for ALL users that have access to an account, regardless of additional accounts or permissions they may have. The functions previously available only affected the security preferences of the user performing the functions, making it difficult to enforce a policy. These new Security Group options enable an administrator to ensure that users’ security preferences adhere to a security policy, and when they don’t, they can forcibly enact them.
The biggest design change that users need to be aware of moving forward is a policy being set at the Account-Level vs. the User-Level. To simplify this design as easily as possible, the Account-Level settings will always take precedence over the User-Level preference. Taking into consideration that users can have access to multiple accounts at the same time, when this occurs, whichever setting between the multiple accounts has the lowest value configured will take precedence. This doesn’t mean that each setting will then be taken from the same Account; it will still be on a case by case for each setting, and each Account-Level configured value for that setting.
-
Please note that only users belonging to the following Groups can make changes to the Security Preferences details.
-
Primary User (Owner)
-
ADMINISTRATIVE group
-
SECURITY-ADMINISTRATION group
-
These fields are completely optional, and are designed to provide a way to enforce security preferences. Click the Save button to apply any changes or updates made to these fields.
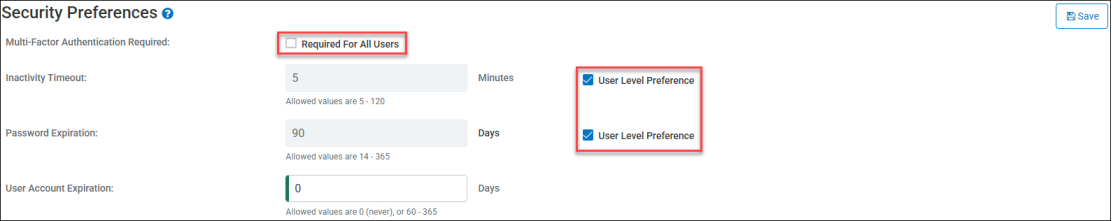
Multi-Factor Authentication Required
This setting enforces Mandatory Multi-Factor Authentication (MFA) for all users. If the Required for All Users box is checked, users need to enable either SMS Multi-Factor Authentication or QR Code Multi-Factor Authentication on their accounts.
Once enabled, users that do not have an MFA type configured on their account will see the following screen when they log in.
|
|
If deselected, each user’s deferral count will be reset to zero and they will no longer be required to use MFA to log into their account. |

Click the OK button to select the MFA type the user wants configured for their account.
|
|
If a Mobile number is not already configured for the account, an error will occur and the Remind Me Later button needs to be selected to gain access to the portal, to then configure a mobile number. |
Click the Remind Me Later button to defer setting up a Multi-Factor Authentication type on the account. Users that do not complete the mandatory MFA setup process after deferring 3 times will have their accounts suspended.
Inactivity Timeout
This setting determines after how many minutes a user will be logged out of their account for inactivity on the UltraDNS Managed Services Portal.
-
An integer value between 5 and 120 is allowed.
To allow users to configure their own Inactivity Timeout value, check the User Level Preference checkbox, otherwise, the value configured here will be applied to every user in the account.
Password Expiration
This setting determines after how many days a user will be required to change their password.
-
An integer value between 14 and 365 is allowed.
To allow users to configure their own Password Expiration value, check the User Level Preference checkbox, otherwise, the value configured here will be applied to every user in the account.
User Account Expiration
This setting determines after how many days of not logging in, a user's account will be set to Inactive, and they will not be able to log into their account without an Administrator activating their accout.
-
An integer value of 0 indicates that user's accounts will never go inactive due to inactivity.
-
An integer value between 60 and 365 is allowed.